Cloud Security & Identity Engineer · Chicago, IL

I secure identities, and the cloud they live in.

I design least-privilege access on AWS and Azure, run hybrid identity across Active Directory, Entra ID and Okta, keep secrets in HashiCorp Vault, and build the detection that catches what slips through. Then I write it down so someone else could rebuild it.

Currently
Working in IT security in Chicago, and building a regulated-bank identity and network lab on the side. Now page
Credentials
AWS Security Specialty · CCSP · SC-300 · Okta Certified Professional and Administrator · Security+ · all eighteen
Education
M.S. Cybersecurity & Digital Forensics, Illinois Institute of Technology · B.Sc. Computer Science & Engineering, University of Mines and Technology
Elsewhere
GitHub · LinkedIn · Email
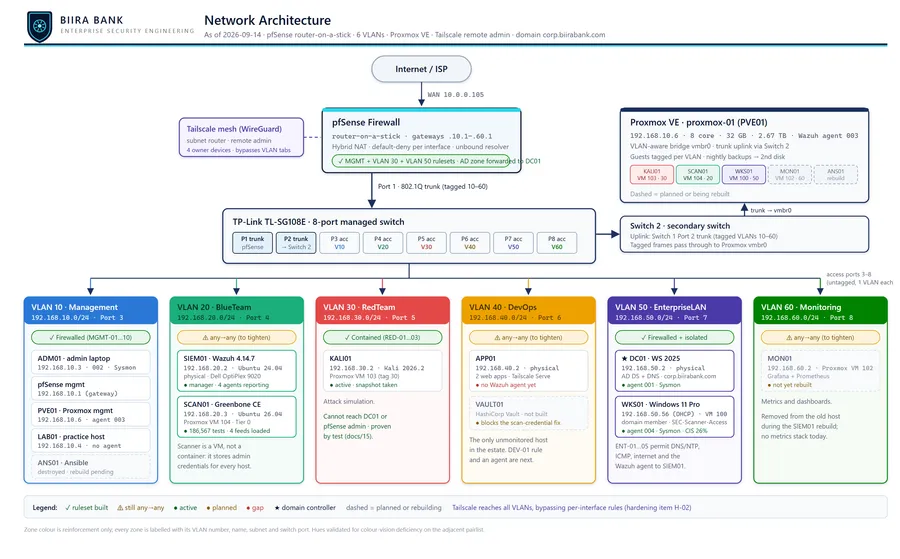
Biira Bank lab network architectureThe internet reaches a pfSense firewall, which trunks on port 1 of Switch 1. Port 2 of Switch 1 trunks to Switch 2, which carries the tagged VLANs to the Proxmox hypervisor. Six VLAN segments hang off the tagged fabric: Management, BlueTeam, RedTeam, DevOps, EnterpriseLAN and Monitoring. The domain controller on the EnterpriseLAN segment reaches Okta and Microsoft Entra ID outbound only.InternetuntrustedFW01 · pfSensegateway on all six VLANsdefault denytrunkSW01 · TL-SG108EP1 trunk, P2 trunkP3 to P8 access, one VLAN eachP2SW02carries the tagged VLANsPVE01 · Proxmox VEone VLAN-aware bridgea guest's segment is one tag802.1Q tagged fabricVLAN 10Management192.168.10.0/24default denyPVE01hypervisorADM01admin laptopANS01rebuildingVLAN 20BlueTeam192.168.20.0/24permissiveSIEM01Wazuh managerSCAN01GreenboneVLAN 30RedTeam192.168.30.0/24default denyKALI01attack hostVLAN 40DevOps192.168.40.0/24permissiveAPP01web appsVAULT01plannedVLAN 50EnterpriseLAN192.168.50.0/24default denyDC01corp.biirabank.comWKS01domain joinedVLAN 60Monitoring192.168.60.0/24permissiveMON01rebuildingAD Agent, outbound onlyOkta · Microsoft Entra IDnothing inbound reaches DC01trunk, all VLANs taggedaccess, one VLANtagged to a guest, or outbound onlyruleset written, three of sixstill permissiveInternetuntrustedFW01 · pfSensegateway on all six VLANs, default denySW01 · SW02P1 trunk to the firewall, P2 trunk to SW02, then ProxmoxVLAN 10 · ManagementPVE01 · ADM01 · ANS01default denyVLAN 20 · BlueTeamSIEM01 · SCAN01permissiveVLAN 30 · RedTeamKALI01default denyVLAN 40 · DevOpsAPP01 · VAULT01permissiveVLAN 50 · EnterpriseLANDC01 · WKS01default denyVLAN 60 · MonitoringMON01permissiveDC01, VLAN 50, outboundOkta · Microsoft Entra IDreached from DC01, never the other wayruleset written, three of sixstill permissive
Current state. Two switches: port 1 of Switch 1 trunks to pfSense, port 2 trunks to Switch 2, which carries the tagged VLANs to the hypervisor. Physical hosts land on a single-VLAN access port; a guest's segment is one tag on its virtual NIC.
Selected work

Labs built like production, documented like an audit.

All projects
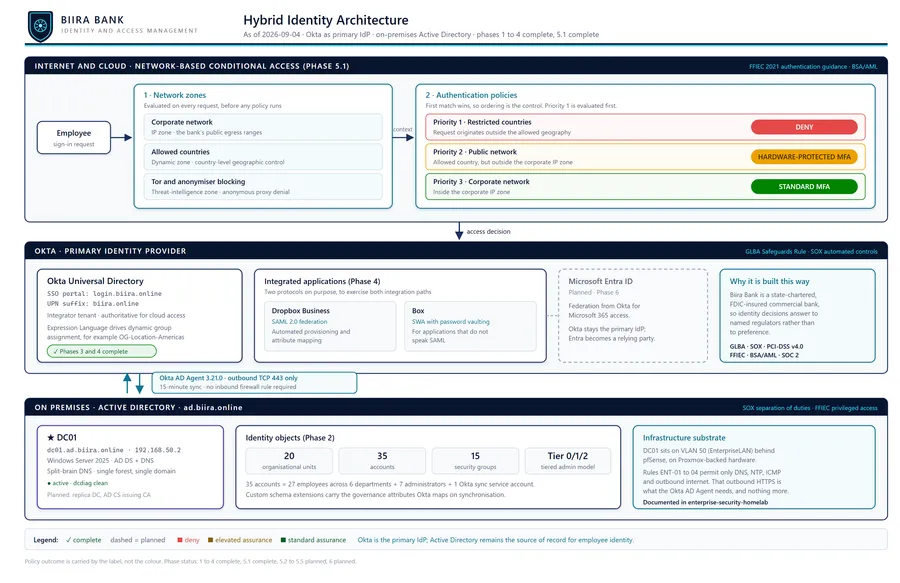
Hybrid identity architecture diagram: network zones and authentication policies above Okta and Entra ID, with Active Directory on premises reached by the Okta AD Agent
Identity · Hybrid identity · Biira Bank

Enterprise IAM Lab: Hybrid Identity for a Regulated Bank

On-prem Active Directory with a tiered admin model, federated to Okta Workforce Identity and Microsoft Entra ID over SAML, OIDC and SWA, with network-aware conditional access and graduated MFA. Built to the regulatory drivers a real bank would have to satisfy, and now being rebuilt on a new forest from a written decision record.

Active DirectoryWindows Server 2025Okta Workforce IdentityMicrosoft Entra IDSAML 2.0OIDC
Read the case study
Network architecture diagram: internet, pfSense, two switches and six VLAN security zones with firewall status, the hosts in each zone and their Wazuh agents
Infrastructure · Detection · Biira Bank

Enterprise Security Homelab

A six-VLAN, default-deny network for a fictional regional bank: pfSense, managed switching, a Proxmox hypervisor on a trunk port, a Windows Server 2025 domain controller, a Wazuh SIEM with four agents and its own detection rules, a Greenbone scanner whose identity is administrator on member machines and nothing on the domain, a first finding found, fixed and proved closed, and every firewall rule justified and mapped to a NIST control.

pfSense802.1Q VLANsProxmox VEWindows Server 2025Wazuh 4.14Sysmon
Read the case study
Writing

Notes from the lab and the study desk.

Written as I go, so they contain the mistakes as well as the fixes. 4 series so far: AZ-900, from zero to 873, HashiCorp Vault, hands on, Enterprise homelab notes, Identity certifications.

All writing
Credentials

Eighteen, weighted toward identity and cloud security.

All credentials